vCISO / Virtual CISO
A senior security executive for two to eight days a month — enough to own the risk register, roadmap and board conversation.
- Ranked, costed risk register
- 12-month security roadmap
- Quarterly board reporting
One system for payroll, attendance, and leave — built around Philippine labor rules so HR stops chasing spreadsheets.
Request a Demo Not sure where to start?Get a starting budget
One system for payroll, attendance, and leave — built around Philippine labor rules so HR stops chasing spreadsheets.
Request a DemoNot sure where to start?Get a starting budgetGovernance, monitoring and response sized for organisations that need a real security capability but not yet a forty-person one — built around Philippine regulatory obligations from the start.
Start with one line or combine several. Each is scoped with you before work begins.
A senior security executive for two to eight days a month — enough to own the risk register, roadmap and board conversation.
Twenty-four hour detection and response from our own security operations teams in Makati and Cebu.
Gap assessment, records of processing, filings and DPO support — privacy compliance finished, not perpetually in progress.
A retained response team with Philippine-based forensics and a two-hour response commitment.
Not sure what it’ll cost?Get a starting budget
Our Process
No recommendations before we know what you have, and every control leaves evidence an auditor can read.
Technical assessment, policy review and interviews to establish what is actually true today.
A ranked risk register with cost and effort against each item, agreed with your exec team.
Controls, tooling and process rolled out in the agreed order, with evidence captured as you go.
Detection tuned monthly, hunts scheduled, alert volume trending down rather than up.
Board reporting, tabletop exercises and an annual independent review.
Case Study
A vCISO engagement plus managed monitoring for an agency with no prior security operations coverage.
Case Studies
Cybersecurity engagements — the problem, what we did and what changed.
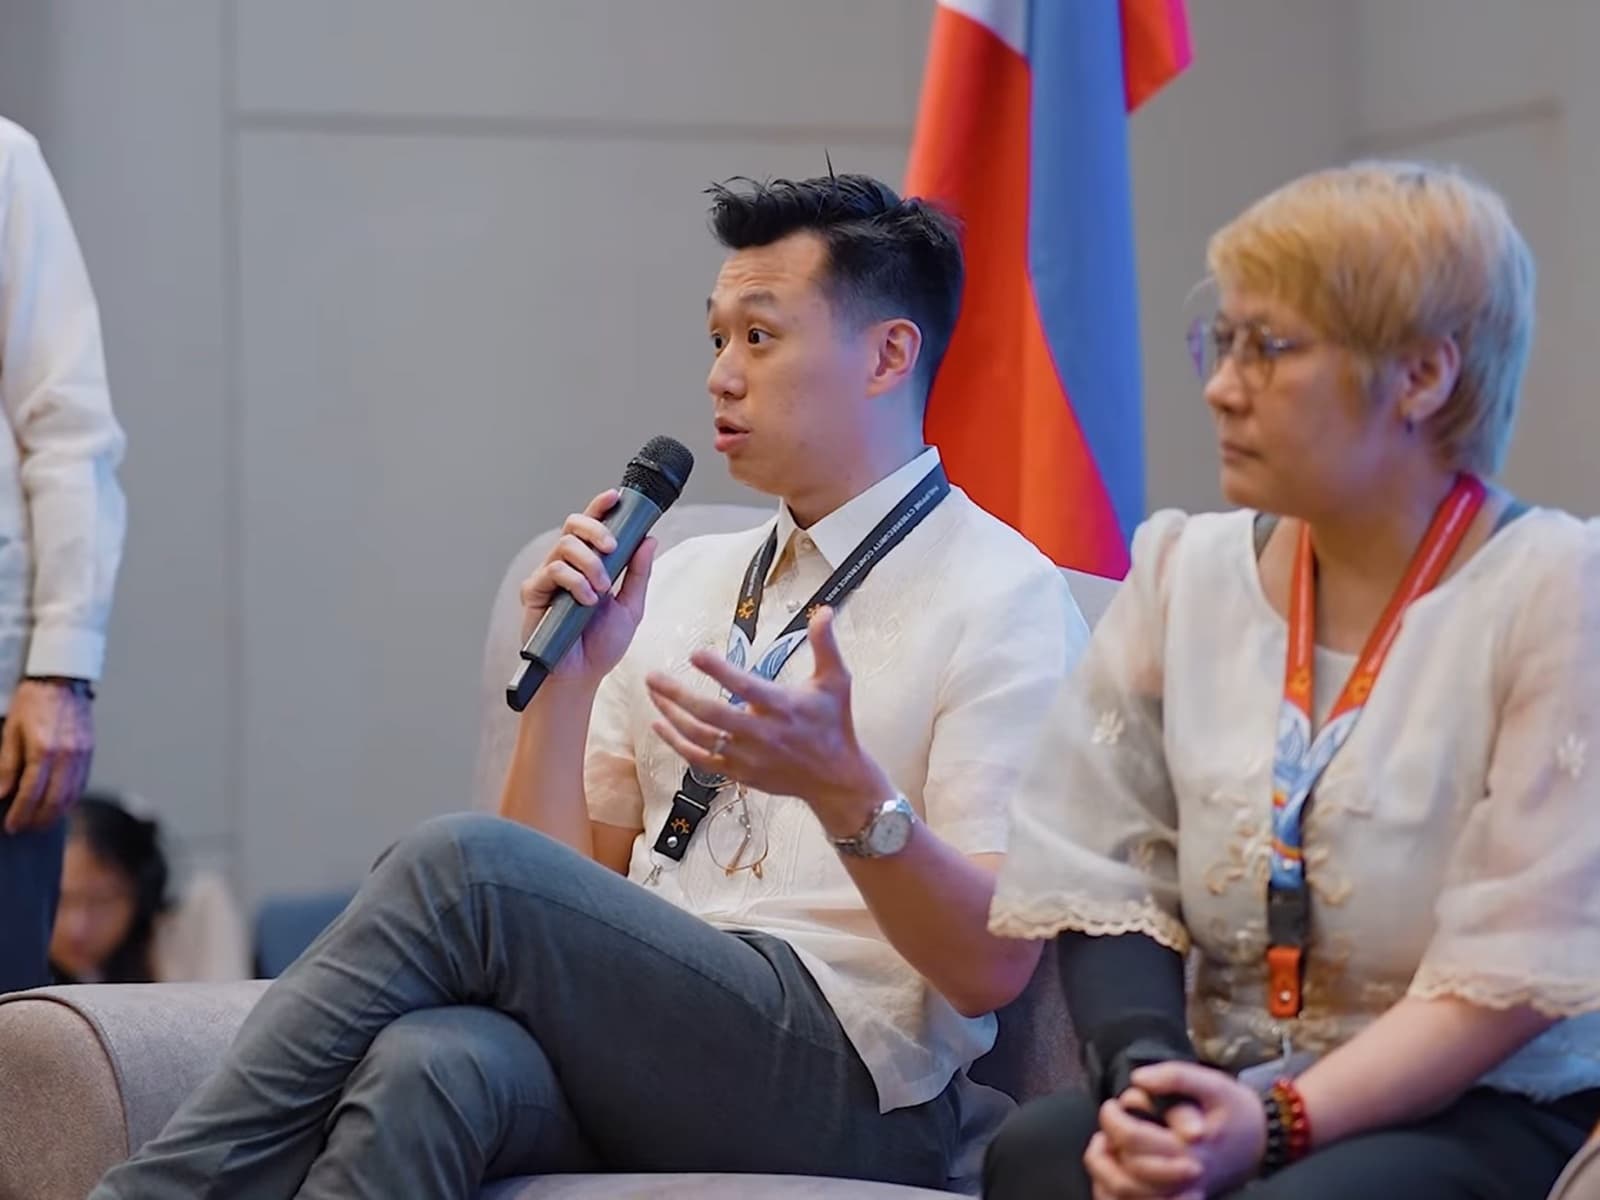
Cybersecurity talent, practical resilience, and affordable protection for Philippine businesses: Springboard's perspective from Philippine CyberCon 2026.
Artificial intelligence has quickly become part of everyday business. Whether it’s helping teams automate repetitive tasks, analyze data faster, or improve customer experiences, AI is proving that it’s more than
In an increasingly connected world, cyber threats have evolved from isolated disruptions into systemic risks. Today, these risks can impact entire organizations, industries, and even economies.
No. We give them a security function to work with, and we take the on-call burden they should never have had.
We implement what fits and we disclose every commercial relationship. Where you already own licences, we use them.
Yes, though retained clients get the two-hour commitment. Call the number on the contact page and say it is live.
We draft the notification and manage the 72-hour clock alongside your counsel. We have been through the process, including the follow-up questions.